AI Security Interviews
Protecting the systems we build.
AI security taught from the fundamentals up, and the interview loop it leads to: trust boundaries and identity, prompt injection, agent and MCP security, red teaming, model supply chains and governance.
- 600worked interview questions
- 153lessons to study
- 806practice-test items
- 17security topics
- 4courses
- 34company interview guides
Counted from the published library on 9 November 2026.
Who it prepares.
- AI Security Engineer
- AI Red Teamer
- Product Security Engineer
- ML Security Researcher
What it goes deep on.
- LLMs & RAG
- Agents & tool use
- Evaluation
- Cloud, Kubernetes & infrastructure
- AI security & safety
- Training & fine-tuning
- Inference & serving
- GPUs & accelerators
- MLOps, DevOps & SRE
- System design
- Behavioral & customer rounds
A dedicated topic, course or trackCovered within other topics
Trace an agent action through its trust boundaries.
Start here when the role asks you to identify how an AI system can be misused and design controls that can be tested. Keep the model's proposed action separate from the identity and authority used to execute it.
Finish with a small threat model and a control-verification plan for an isolated exercise environment.
Try it before reading the answer.
- 1. Draw the path from a user request to a tool's side effect. Mark where identities, permissions, and untrusted inputs cross boundaries.
- 2. Choose a revocation scenario. Account for cached decisions, issued credentials, and work already dispatched.
- 3. Write a defensive test plan: what should be denied, what evidence demonstrates denial, and which effects require reconciliation.
Practise revoking an agent's access
Premium answer on AI Security Interviews. Access follows the destination platform's rules.
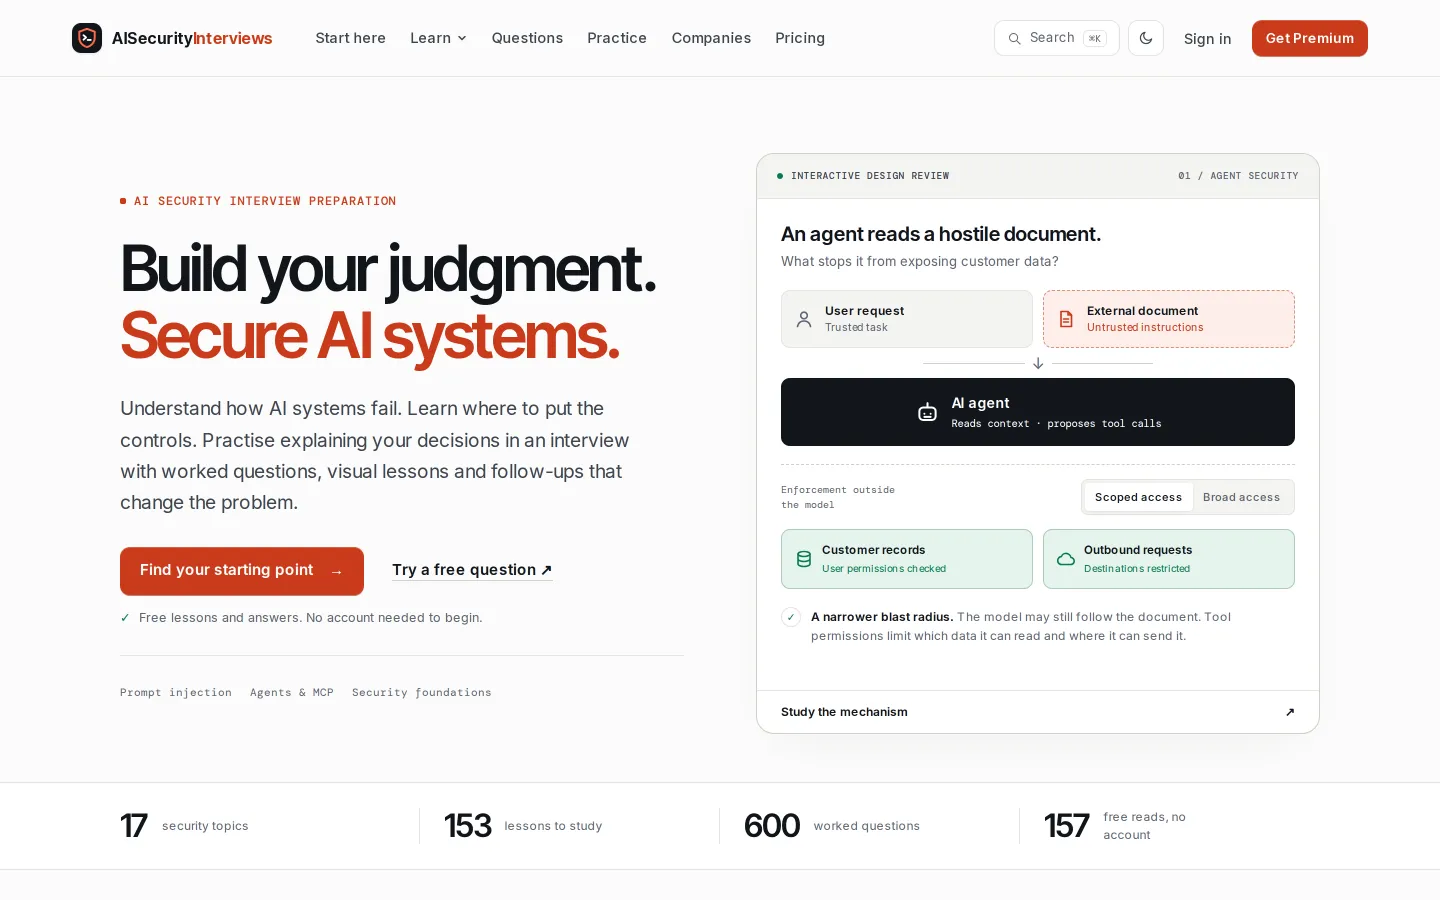
Build your judgment. Secure AI systems.
A look at what you work with on aisecurityinterviews.com.
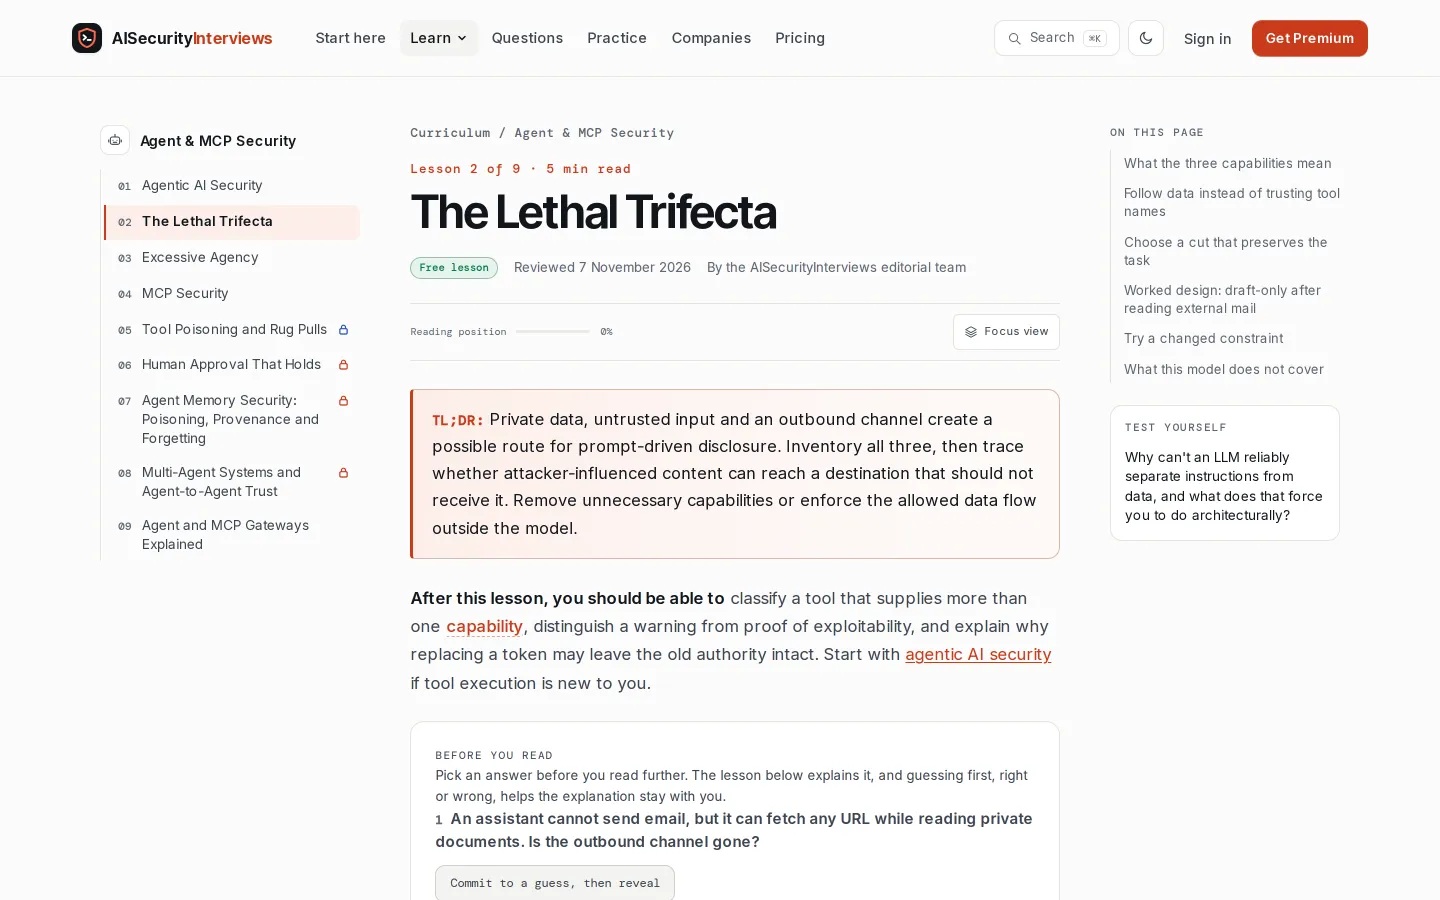
A lesson on the lethal trifecta, with a stepped diagram
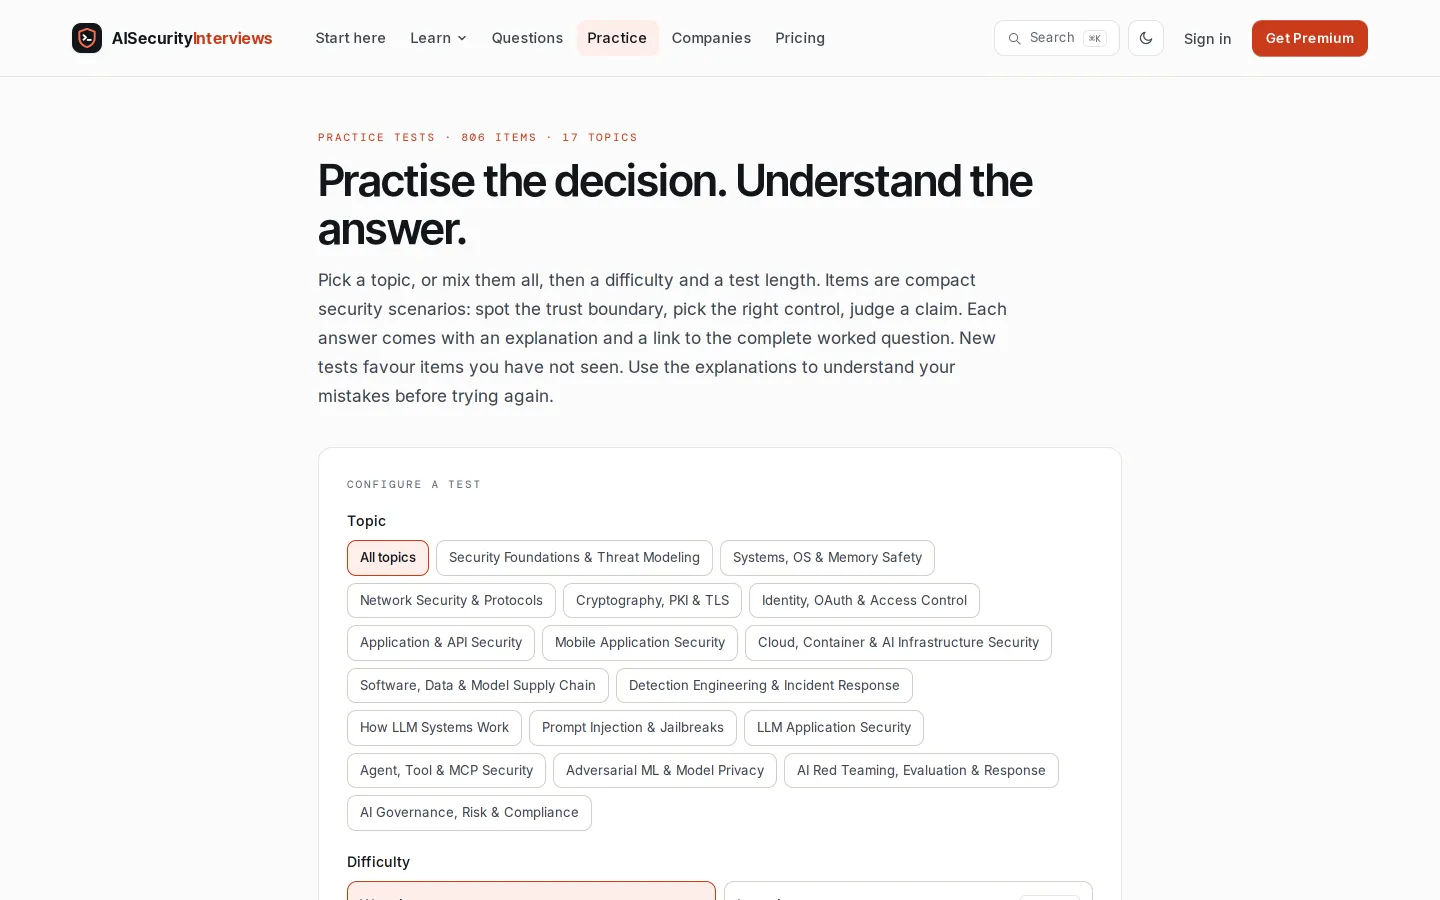
Practice tests across 17 security topics
17 interview topics
- Threat modeling
- Systems, OS & memory safety
- Network security
- Cryptography, PKI & TLS
- Identity, OAuth & access control
- Application & API security
- Mobile application security
- Cloud & AI infrastructure security
- Software, data & model supply chain
- Detection & incident response
- How LLM systems work
- Prompt injection & jailbreaks
- LLM application security
- Agent, tool & MCP security
- Adversarial ML & model privacy
- AI red teaming & evaluation
- AI governance, risk & compliance
What Premium unlocks.
- Every answer across all 17 topics, first-round to staff-level
- All 122 curriculum lessons and all 31 course lessons
- Practice tests at every level, plus adaptive sessions
- Animated diagrams with a self-check on every lesson
- What-if follow-ups and scoring criteria
Free answers and lessons in every topic stay free. Premium opens the rest.
7 more platforms.
- FDE InterviewsForward deployed engineering
- AI Infra InterviewsThe infrastructure behind intelligence
- Applied AI PrepFrom models to meaningful products
- DevOps Interview PrepEngineering that keeps the world running
- AI Interview TrainingA foundation for the AI era
- AI PM InterviewsProduct judgment for the AI era
- Inference InterviewsEvery token. Every engineering decision.